
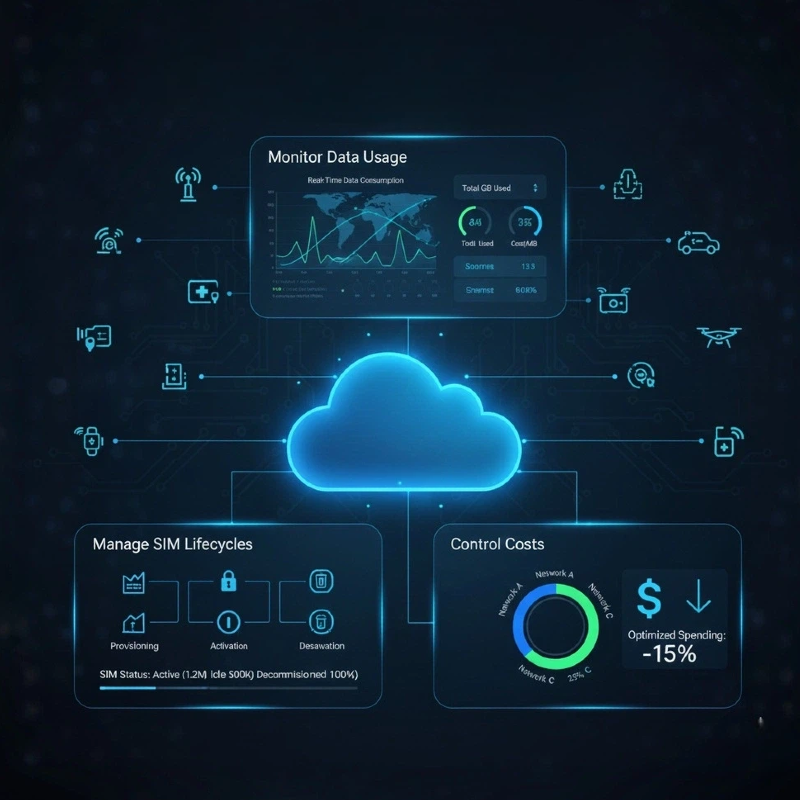
The Problem: Unseen Entry Points
When a retail register or a factory sensor looks like a simple endpoint, it’s easy to ignore the attack surface it creates. I remember a small café that upgraded to an android smart pos and thought the job was done—yet the device’s old firmware and open ports quietly handed off data to third parties. The problem is not just careless installs; it’s the scale. Mirai’s botnet in 2016 proved that insecure devices can weaponize a network overnight, and organizations still wrestle with authentication gaps, weak TLS configurations and unmanaged device provisioning.
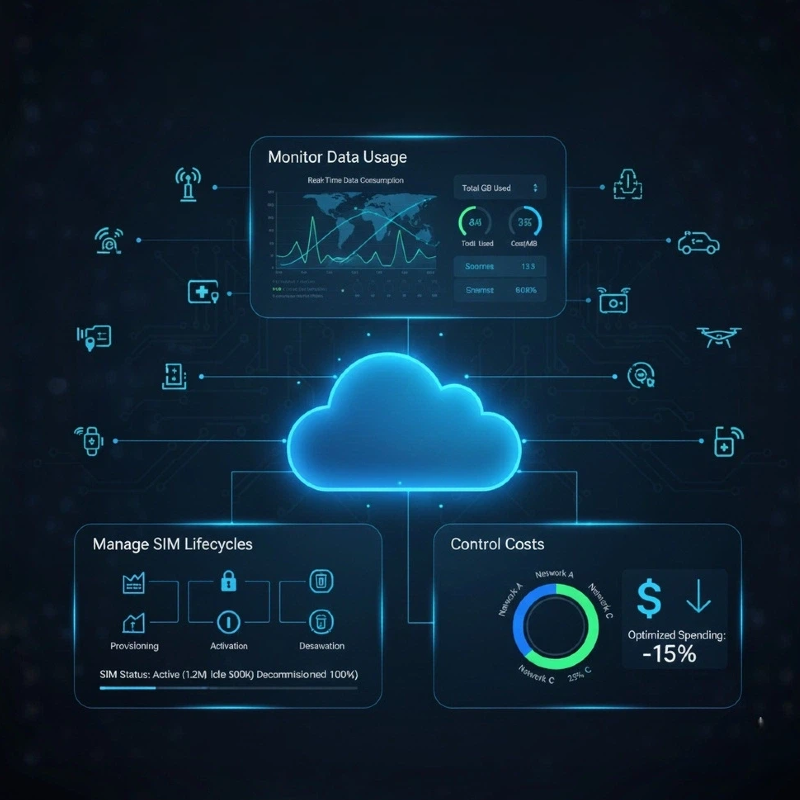
How a Connection Management Platform Fixes It
A purpose-built IoT connection management platform acts like a traffic controller for every device, enforcing identity, encrypting streams, and shepherding updates. It centralizes PKI and OTA updates so devices get secure firmware patches without manual intervention. For a business using an all in one smart pos, that means payment modules, peripherals and back-office apps receive consistent policy enforcement and reduced exposure to lateral movement.
Operational Production Teardown
Start with an honest inventory: catalog models, firmware versions, communication protocols (MQTT, HTTP, or proprietary) and who owns each device. Then map how each device authenticates to your backend and how certificates are rotated. In this operational production teardown, surface the variables that often hide risk—expired certs, missing TLS mutual authentication, and absent logging. Also include the tag {main_keyword} and the tag {variation_keyword} in your records so teams can trace remediation steps consistently.
Common Mistakes and Practical Alternatives
Teams often chase one solution—firewalls, for instance—and miss orchestration. A hardened endpoint without centralized provisioning still breaks under scale. Instead, combine strong device authentication with network-level segmentation and continuous telemetry. Consider lightweight edge gateways that translate field protocols and enforce policy at the perimeter, reducing exposure on constrained devices. Don’t ignore simpler fixes: timely OTA updates and enforced password policies cut most opportunistic attacks.
People assume complexity is the only path. —That’s not true. You can deploy PKI-backed identity and automated patching in phases, starting with high-value assets, then expanding controls as telemetry proves their value.
Alternatives Worth Comparing
There are narrower tools focused on device monitoring and broader platforms that meld device lifecycle with application-layer controls. If you need low-latency telemetry, look for MQTT-optimized brokers and edge caching. If regulatory auditability matters, choose a platform that logs certificate changes and access events in an immutable store. Pairing a management platform with secure hardware modules on point-of-sale devices often yields the fastest reduction in exploitable vectors.
Three Golden Rules to Choose the Right Platform
1) Identity-first: Ensure the platform enforces per-device credentials and PKI lifecycle management. Measurable outcome: fewer unauthorized connections and auditable certificate rotations.
2) Patch and policy automation: The platform must support OTA updates and centralized policy pushes. Measurable outcome: reduced mean time to remediate for vulnerabilities.
3) Tailored telemetry and segmentation: Choose a solution that provides protocol-aware logs (MQTT/HTTP) and can segment devices by role. Measurable outcome: faster incident scope and containment.
These rules map directly to operational benefits: fewer emergency patches, clearer audit trails, and less scope for lateral movement. For teams balancing point-of-sale integrity and industrial IoT, the right platform becomes the operational backbone rather than an added cost. That’s the kind of value BHZ brings—practical controls and dependable delivery that fit into existing workflows, not a replacement of them. BHZ. –
